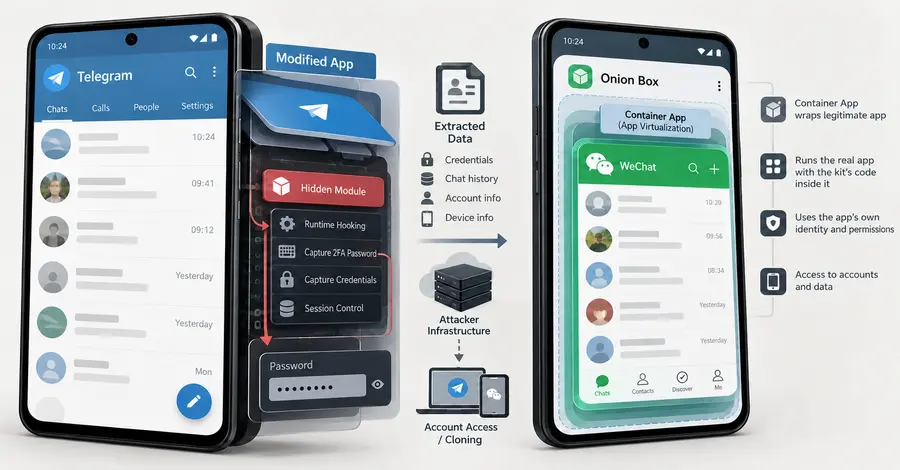
This kit achieves control over both Telegram and WeChat accounts. It functions by embedding its code within functional duplicates of these two applications.
The spyware's reach is limited to specific installation vectors. These include users installing the modified copies outside of official application marketplaces. Alternatively, the attack targets individuals who execute WeChat within a container application developed by the kit creators.
The component of uCreator designed for Telegram aligns with Baohuo. Baohuo is noted as a backdoor previously identified by Doctor.
This development highlights ongoing risks associated with third-party application distribution channels for mobile platforms. Security assessments must remain vigilant regarding code injection into commonly used communication utilities.