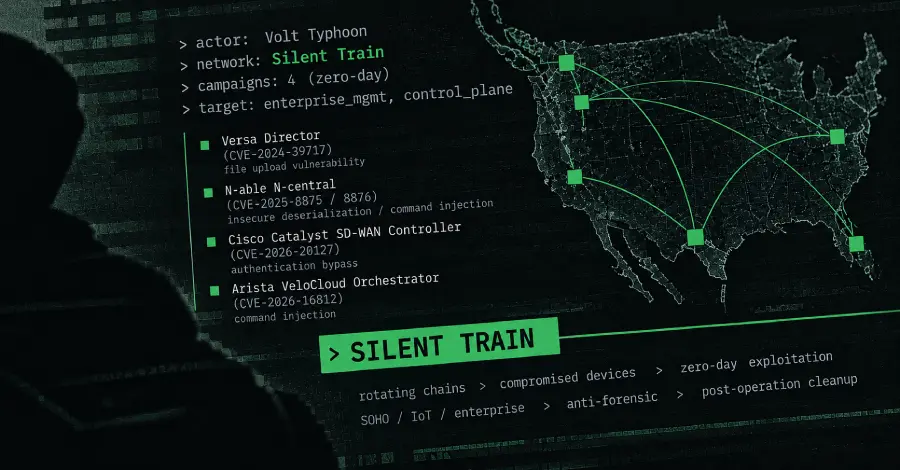
A covert access network named Silent Train, which is now defunct, has been linked to the China-nexus cyber espionage group Volt Typhoon, utilizing it for strategic access and zero-day exploitation efforts.
Lumen Technologies Black Lotus Labs reported that Silent Train, which was initially detected toward the close of 2023, operates by employing shifting sequences of compromised infrastructure found in SOHO, IoT, and enterprise environments.
This attribution indicates a sophisticated operational capability employed by Volt Typhoon, leveraging diverse and transient network footholds for advanced persistent access.
The utilization of rotating chains across various infrastructure types suggests an adaptation strategy by the threat actor to maintain persistence while evading detection mechanisms targeting static access points.
Why it matters
This indicates a sophisticated, multi-layered approach to gaining strategic access across diverse infrastructure. Operators must assess how this method could bypass traditional perimeter defenses using compromised endpoints.