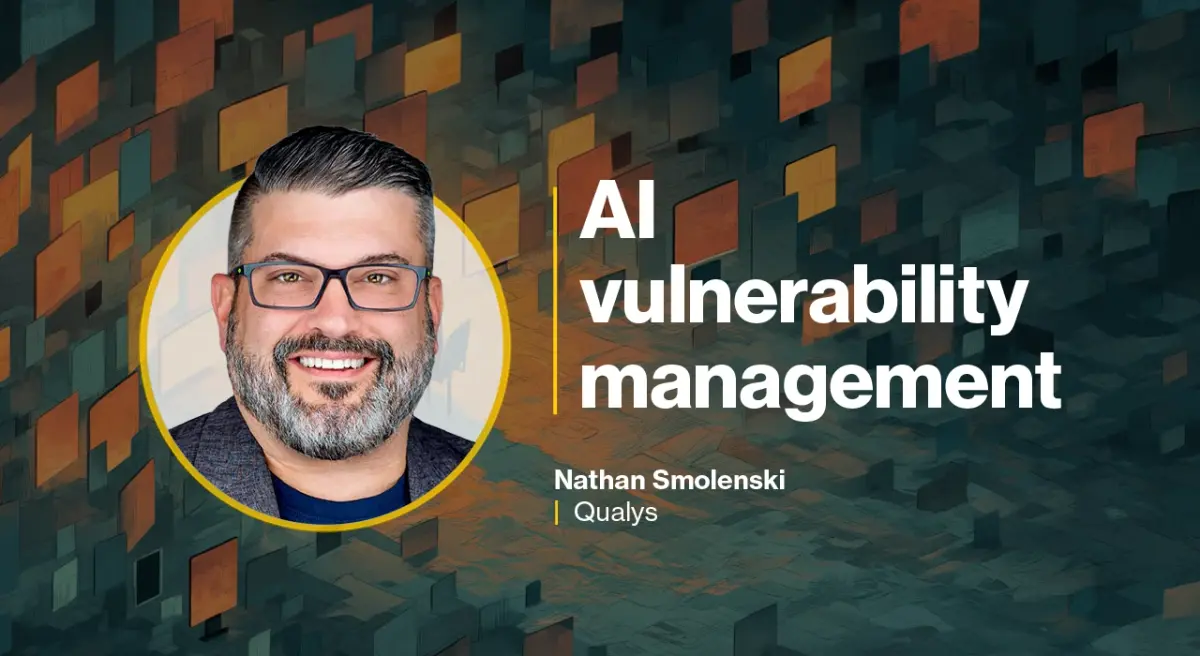
In an interview with Help Net Security, Smolenski elaborated on why CISOs ought to monitor the average window of exposure, rather than relying on standard MTTR metrics.
He further noted that only a minor percentage of vulnerabilities that are disclosed—less than one percent in 2025—present an actual, active risk.
Smolenski also detailed mechanisms for fostering confidence in automated remediation. These mechanisms include asset tiering, human review stages, and rollback procedures.
The discussion, featured in Help Net Security, addresses the challenges presented by proliferating AI-identified security gaps.
This focus on exposure windows and tiered remediation reflects a broader industry shift in how risk management frameworks are being adapted to modern, high-velocity threat landscapes.