Crucially, none of these providers were aware of the intrusion until researchers alerted them.
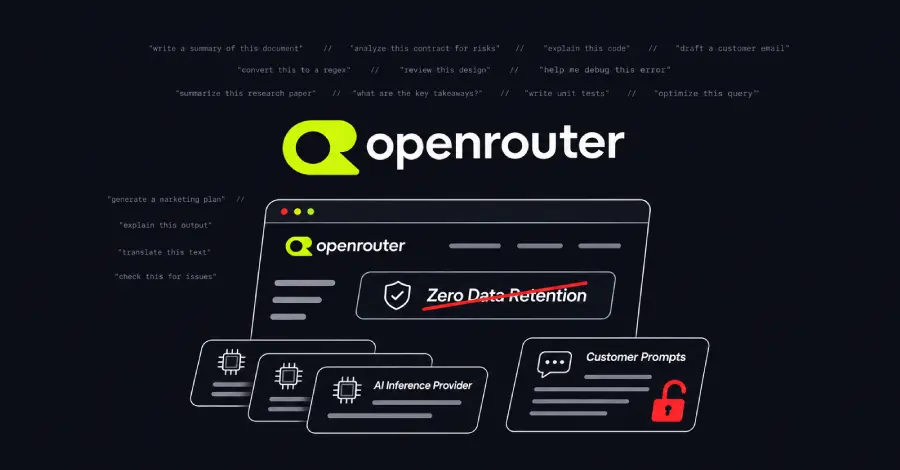
Some of the compromised requests were associated with the Zero Data Retention setting, which is intended to ensure a prompt is never kept.
OpenRouter, which functions as a gateway directing client AI requests to a selection of providers, has taken action.
The platform has consequently dropped three providers following the discovery of this security lapse.
This incident highlights significant vulnerabilities within the infrastructure supporting AI model access.
Such findings underscore ongoing concerns among market participants regarding data governance and security assurances provided by third-party inference services.
Why it matters
This incident highlights significant security vulnerabilities within AI hosting infrastructure, directly impacting data privacy for users. Operators must scrutinize the security posture of their AI backend providers, especially concerning data retention policies.