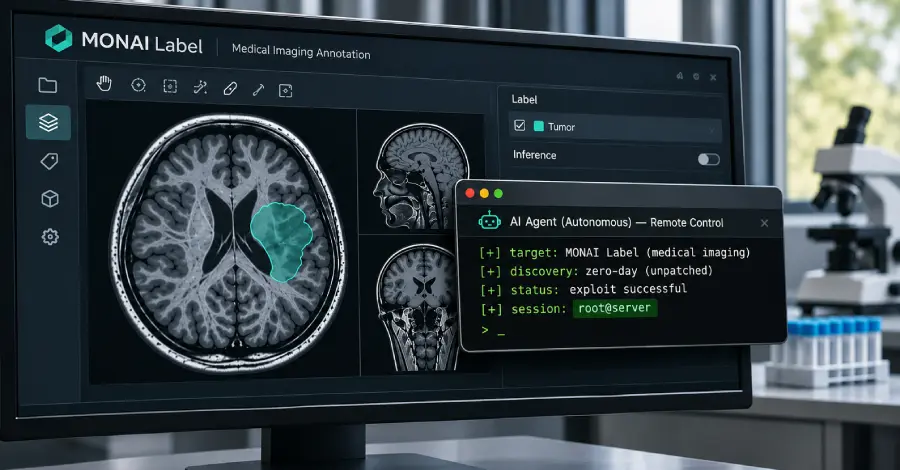
Amazon Threat Intelligence reported this week that autonomous AI agents, allegedly operated by threat actors linked to China, discovered a novel vulnerability within MONAI Label, an open-source server designed for medical imaging. This security lapse permitted unauthorized access, specifically enabling the attackers to achieve root privileges on a university server. The vulnerability in question allows an adversary, even one lacking any established account credentials, to write files situated outside the designated storage directory of the server. Furthermore, this issue is present in MONAI Label versions up to and including 0.8.5 when deployed using the standard configuration.
This incident highlights the evolving threat landscape where sophisticated automation tools are being leveraged to discover critical vulnerabilities within specialized infrastructure components. Institutional participants must recognize that the integration of advanced AI into offensive tooling presents a novel challenge to platform security postures.
Why it matters
This incident highlights the evolving threat landscape where AI is used to automate vulnerability discovery against critical infrastructure. For operators, this emphasizes the urgent need to patch open-source platforms like MONAI Label to prevent unauthorized root access.