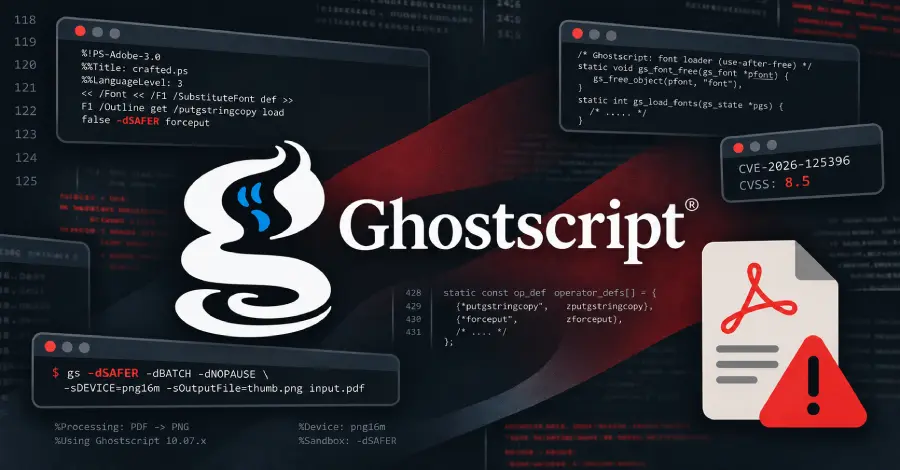
This flaw permits the execution of commands on the server handling the file.
Ghostscript functions as an interpreter utilized by numerous Linux servers. Its role involves transforming uploaded media such as PDFs, PostScript files, and images into different formats.
Frequently, applications interact with Ghostscript without making a direct invocation of the interpreter.
The security firm pwn.ai demonstrated this week that a standard file upload could exploit this weakness.
This development highlights risks associated with file processing components integrated into server infrastructure.
The ability for an uploaded file to trigger remote code execution via a sandbox escape represents a significant operational security concern for platform operators.
Why it matters
Since many server applications use Ghostscript for file conversion, this RCE vulnerability presents a significant risk to infrastructure security. Operators must ensure their systems are patched immediately to prevent unauthorized command execution via file uploads.