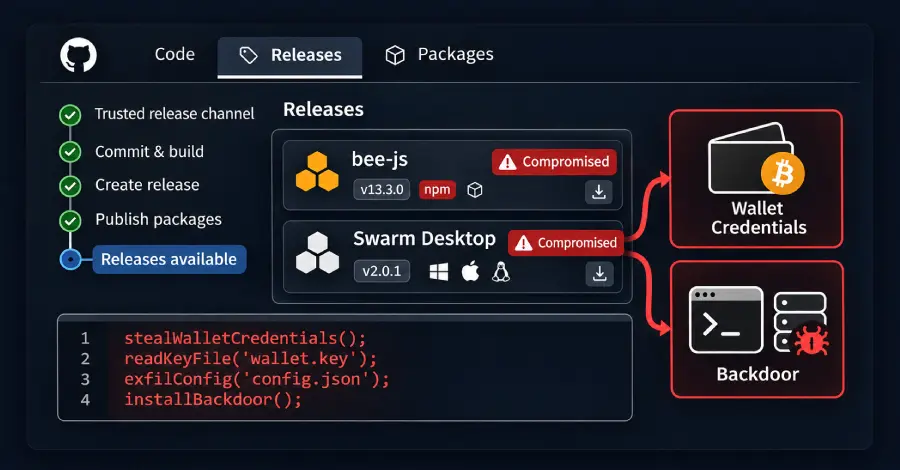
Malicious software designed to steal wallet keys and install a backdoor was disseminated by attackers through the Ethersphere project's established release automation pipeline, affecting two utilities for the Swarm decentralized storage network: bee-js version 13.3.0 and Swarm Desktop version 0.56.2.
These compromised releases contain code that executes upon download and runtime, specifically targeting the wallet key maintained by the Swarm Desktop node, in addition to the associated password used to access it.
This incident demonstrates a critical vulnerability in software supply chains, where the integrity of established release mechanisms can be exploited to introduce malicious components into widely used infrastructure tools.
This exploitation of the release automation process highlights significant security risks inherent in the software distribution lifecycle for decentralized network components.
Why it matters
This incident highlights critical supply chain vulnerabilities within decentralized infrastructure tooling. Operators must immediately audit dependencies like bee-js and Swarm Desktop for compromised releases to prevent wallet theft and unauthorized access.