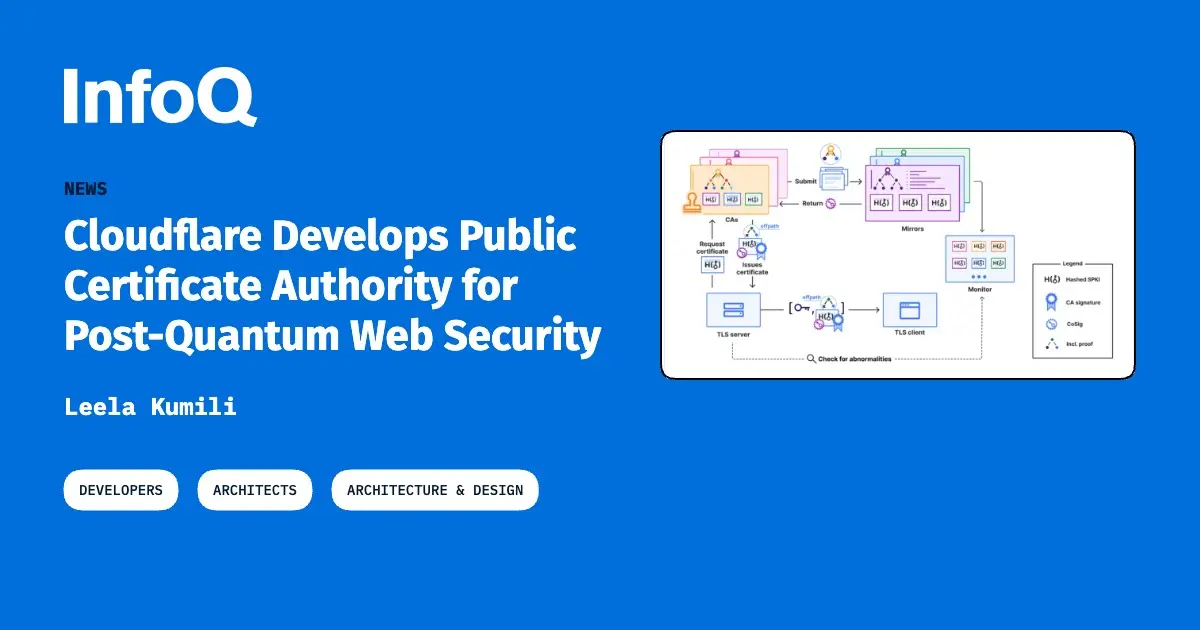
Cloudflare attributed most of the measured improvement to eliminating intermediate certificates; the experiment used classical signatures rather than post-quantum signatures. Building on the approach covered in InfoQ's earlier report, Cloudflare describes how landmark-based verification and independent transparency log cosigners support certificate issuance and verification at scale. The experiment served billions of MTCs to 50% of Chrome Beta 146 for selected domains on Cloudflare's free plan.
Cloudflare wound down the experiment in August 2026 and is developing a public certificate authority (CA) that supports MTC issuance, targeting inclusion in Chrome's quantum-resistant Root Store in early 2027, subject to evaluation. Cloudflare CEO Matthew Prince, in a press release, said: Upgrading the web's security before quantum computers can break it is one of the biggest coordination challenges in the history of the Internet. Post-quantum cryptography creates scaling challenges for the Web Public Key Infrastructure (Web PKI). According to Cloudflare, post-quantum signatures can be about 40 times larger than classical signatures, increasing bandwidth and storage requirements.