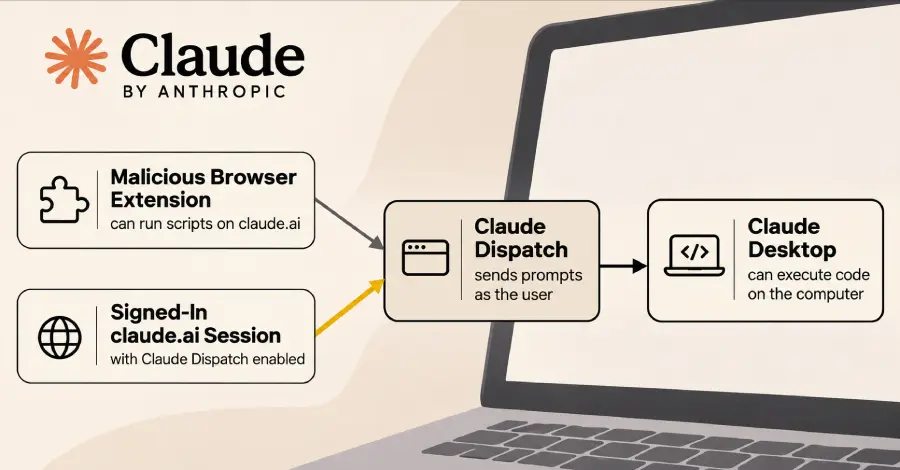
This vulnerability involves a browser extension capable of executing scripts within claude.ai.
The testing revealed that such an extension could compel Claude Desktop to run code on an individual's machine.
The attack vector relies on Dispatch, a Claude capability allowing users to transmit tasks from their mobile devices to Claude Desktop.
The security team noted that the exploitable flaw remains present.
This development highlights risks associated with platform integrations and third-party extensions interacting with AI services.
Market participants must remain aware of potential attack surfaces introduced by features like Dispatch.
Why it matters
This vulnerability presents a significant endpoint security risk to users relying on Claude Desktop. Operators must monitor how third-party extensions interact with platform features like Dispatch to prevent unauthorized code execution.