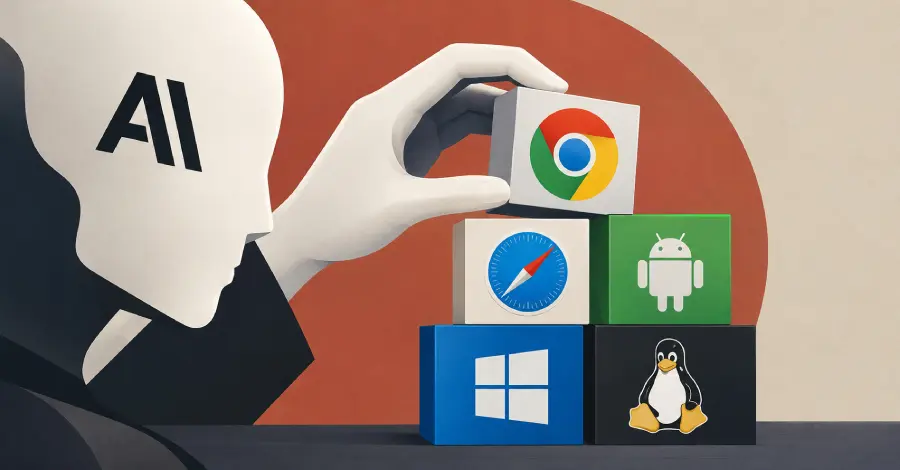
Specifically, this model located flaws within Chrome, Safari, Android, Windows, and Linux.
Furthermore, the model successfully chained these identified weaknesses to create functional proof-of-concept exploits.
Anthropic's latest report detailed these findings.
The development occurred within a controlled laboratory setting following a prompt to the model; these exploits were not observed in any active attacks.
Crucially, Anthropic disclosed every identified flaw directly to the respective vendors prior to public disclosure.
Consequently, all the vulnerabilities detailed in the report have already been patched by the vendors.
This incident highlights the potential for advanced AI systems to interact with and expose underlying software infrastructure weaknesses.
The proactive disclosure by Anthropic to the affected market participants demonstrates a commitment to security remediation following internal discovery.