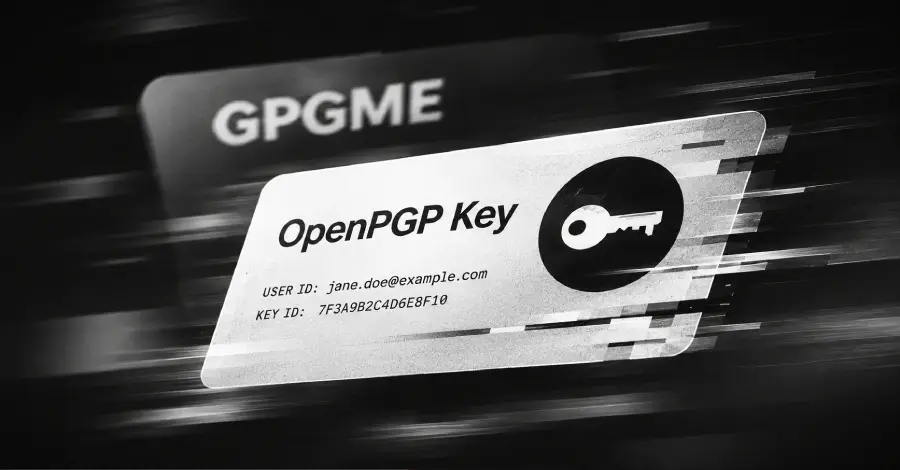
This defect, identified as CVE-2026-129975, enables the potential exfiltration of data from software installations susceptible to it. The vulnerability arises when a malicious OpenPGP key possessing an exceptionally lengthy user ID is processed by GPGME, which subsequently triggers a critical memory error. All applications employing GPGME versions preceding 2.3.0 are impacted by this issue, and patched releases have since been made available.
This security concern underscores the persistent need for rigorous maintenance within cryptographic infrastructure components, as even seemingly benign data structures within key formats can introduce exploitable weaknesses in underlying libraries.
Why it matters
For operators, this vulnerability presents a direct risk to data integrity and confidentiality in applications relying on GnuPG. Immediate patching is necessary to prevent potential data exfiltration via compromised cryptographic libraries.