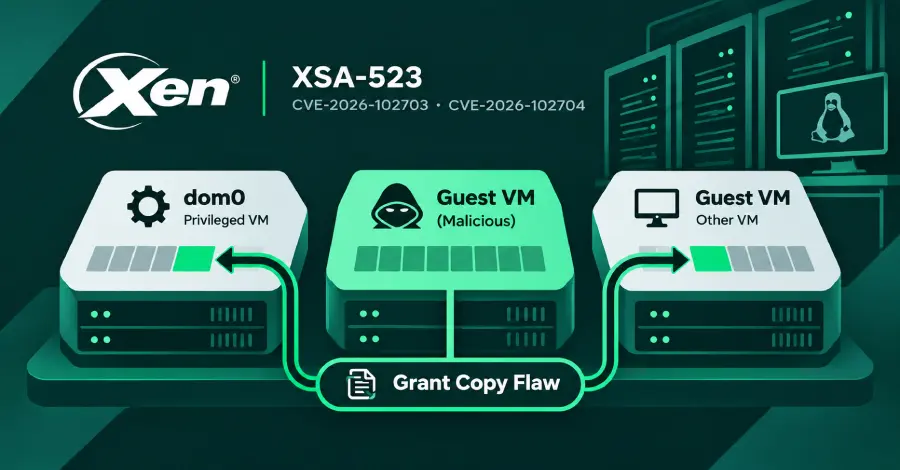
These two flaws permit a malicious guest virtual machine (VM) to access and modify the memory of any other VM residing on the same host. This includes dom0, which inherently possesses comprehensive permissions and oversees the other VMs.
The Xen Project issued an advisory on November 3 detailing these issues.
The advisory confirmed that patches have been released for the affected software.
Currently, there is no established mitigation strategy available for these vulnerabilities.
The scope of the exposure is significant, as all Xen versions dating from 4.6 onwards are susceptible.
This development highlights persistent risks associated with core virtualization layers, impacting the integrity of multi-tenant environments managed by platform operators.
Why it matters
This critical vulnerability directly impacts infrastructure security by allowing unauthorized memory access between isolated virtual machines. Operators running Xen platforms must apply the patches immediately to prevent a single compromised VM from gaining control over the entire host environment, including dom0.