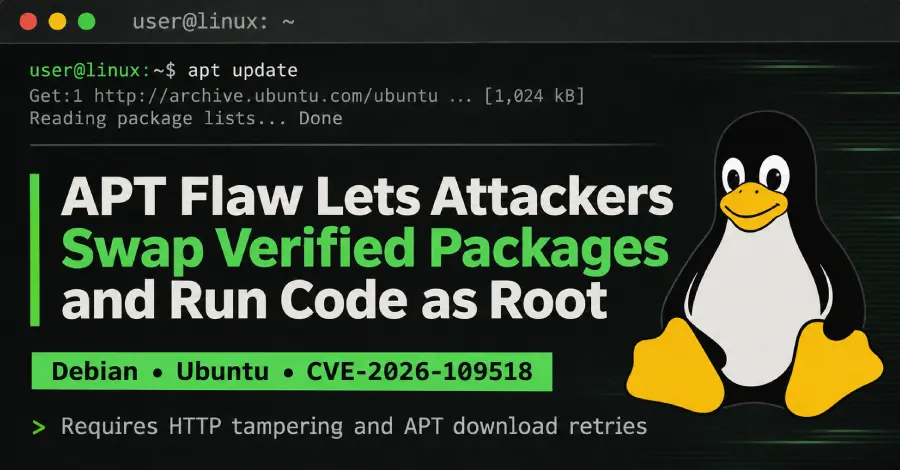
This flaw enables an adversary capable of altering package download streams to substitute an authenticated package with one of their own creation. Consequently, the malicious code introduced by the attacker executes with root privileges.
This exploitation scenario is contingent upon APT initiating a retry of a download that previously failed, a default behavior present starting with Debian 12.
This type of vulnerability in core infrastructure components like package managers highlights persistent risks related to supply chain integrity within open-source software ecosystems.
Why it matters
This vulnerability poses a critical security risk to infrastructure running Debian or Ubuntu systems. Operators must immediately assess their package management configurations to prevent unauthorized root code execution via Man-in-the-Middle attacks.