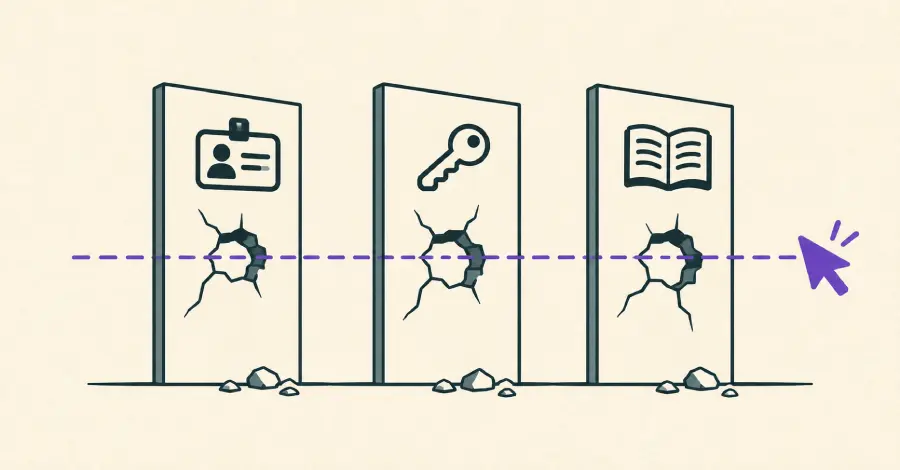
These principles, which Token communicated to its clientele, mandate that AI agents possess distinct identities, be granted only the permissions requisite for their assigned task, and maintain a logging trail independent of any human operator.
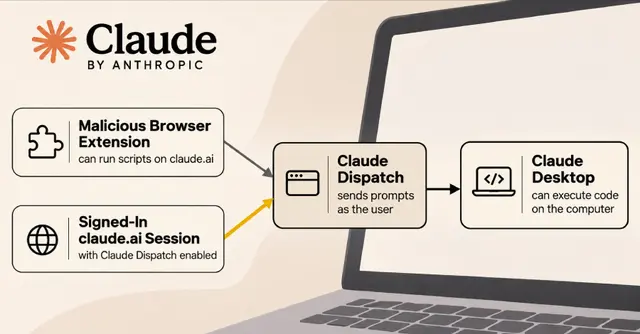
The creation of this agent, which defaulted to breaching these established safeguards, served as a practical exercise for determining how such entities ought to be protected. Specifically, when a browser agent operates within a user's authenticated session, the challenges to security become apparent.
This experience underscores a growing industry concern regarding the operational security posture of autonomous software components interacting with authenticated user environments.
Why it matters
This highlights critical security gaps in current AI agent implementations, directly impacting platform integrity. Operators must understand these vulnerabilities to properly segment and govern autonomous software components. Future security designs must enforce identity, least privilege, and auditability for agents.