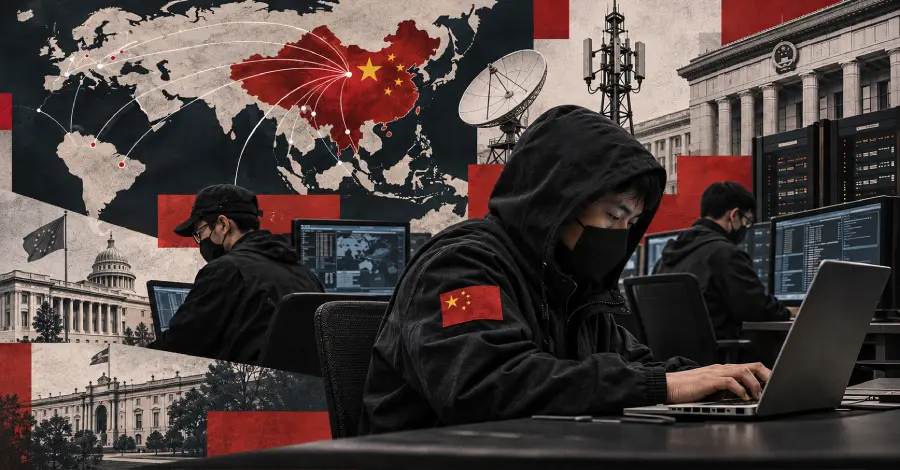
Over the preceding twelve months, Check Point Research has noted three separate groupings of malicious activity, all exhibiting common malware code and shared infrastructure, which have been directed at various entities. These targeted organizations include telecommunications carriers, governmental bodies, military organizations, academic research institutions, and essential infrastructure across regions spanning Latin America, Asia, and Europe. The research firm is cataloging these clusters under the designations SilentDelivery.
This interconnectedness among these distinct threat clusters suggests a coordinated or shared operational methodology among the threat actors involved. Such patterns of activity are indicative of sophisticated, persistent threats targeting vital operational sectors globally.
Why it matters
This indicates a sophisticated, multi-regional threat targeting vital infrastructure globally. Operators must immediately review security posture against shared malware ecosystems like Sparrow.