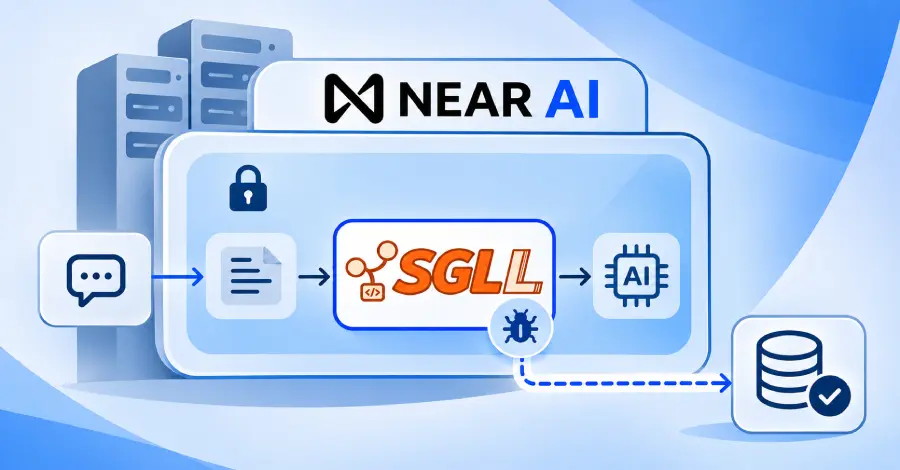
The firm disclosed earlier this week that this breach potentially allowed the attacker to view requests handled by that specific server throughout the day, even those submitted using confidential mode. This confidential mode operates by processing requests within a trusted execution environment (TEE).
The successful exploitation of the remote code execution vulnerability within SGLang led to the compromise of data from approximately 100 users and 18 agents.
This incident highlights the operational risks associated with third-party inference engines, particularly concerning data isolation mechanisms like TEEs, which are critical for maintaining trust in distributed computational platforms.
Why it matters
This incident highlights critical vulnerabilities in open-source inference engines used for AI operations. Readers should monitor how platforms handle RCE risks, especially when sensitive data is processed in trusted execution environments.