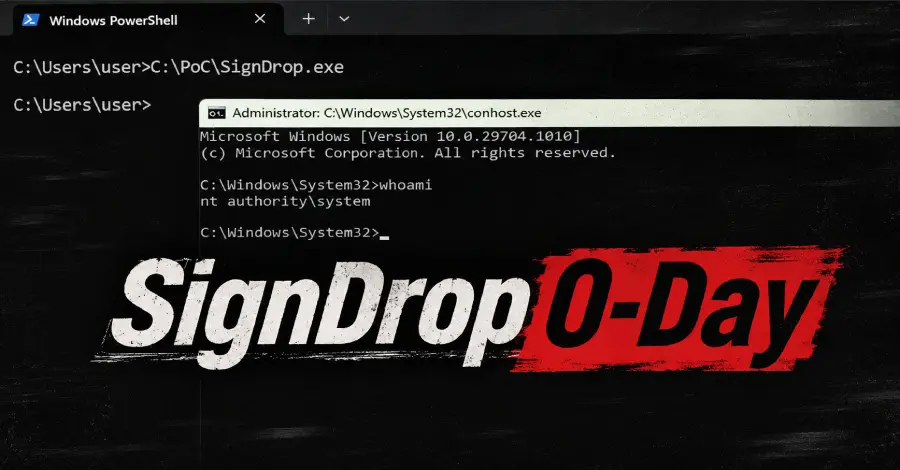
This proof of concept, designated SignDrop, leverages a specific log-authentication feature that was incorporated into the driver during the previous year. The vulnerability stems from the mechanism by which clfs.sys generates associated files when a high-privilege process accesses a pre-arranged log, allowing for control via path redirection.
This development highlights potential weaknesses within core operating system components, specifically related to how file system drivers handle privileged operations and path resolution.
The availability of this exploit code presents a significant risk vector for infrastructure operators managing Windows environments.
Why it matters
This vulnerability presents a critical security risk to Windows environments, potentially allowing unauthorized SYSTEM-level access. Operators must urgently assess their systems for exposure to this dangerous driver flaw. Patching and monitoring for signs of exploitation are now paramount.