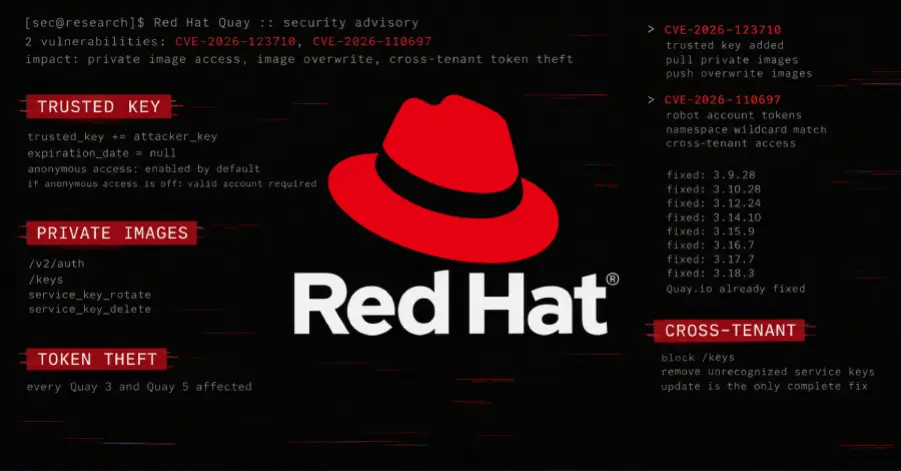
Red Hat has disclosed that a severe vulnerability within Red Hat Quay permits an unauthorized actor gaining access to a Quay registry to both read and modify all private container images across every repository.
The vendor indicated yesterday that even when anonymous access is disabled, any individual possessing a legitimate account can still leverage this weakness. Furthermore, when anonymous access is active, the attacker requires no form of credentials to exploit the issue. Red Hat has subsequently issued patched versions for eight different Quay installations.
This vulnerability underscores inherent risks associated with registry access controls, particularly concerning the integrity and confidentiality of proprietary container artifacts within the platform ecosystem.
The release of fixed builds by Red Hat suggests a necessary remediation cycle across infrastructure deployments utilizing the Quay service.
Why it matters
This vulnerability poses a severe risk to CI/CD pipelines and image integrity within containerized environments. Operators must immediately assess their Quay configurations and apply the released patches to prevent unauthorized data modification or exfiltration.