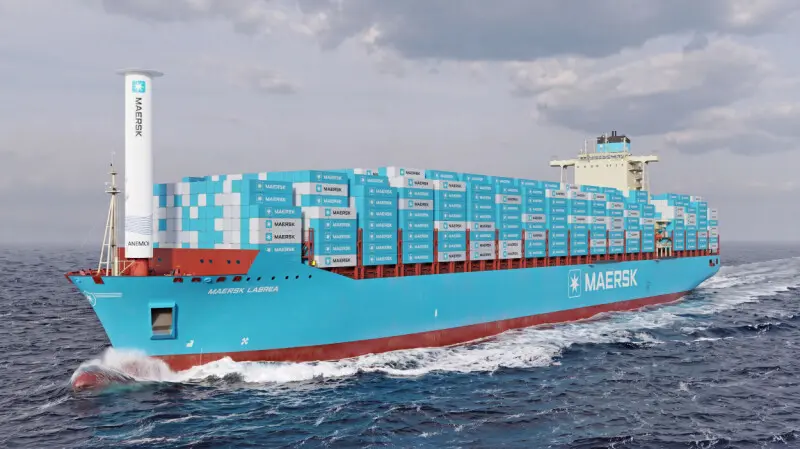
In a statement issued on Wednesday, the Denmark-based shipping, cargo, and logistics giant confirmed it immediately rolled out an investigation into the attack and the affected system was secured. "Our findings so far strongly suggest no sensitive data has been disclosed," the company said. "The incident is isolated to a local system, and we have found no indication that there has been any impact on other Maersk systems or customer and partner systems that connect to Maersk through integrations such as APIs and EDI."
Maersk described the legacy local system as one "from a previous acquisition," and said it does not expect the attack to have an effect on operations. Customers were reassured that they can continue to use Maersk platforms to manage their shipments as usual, and to expect updates from the company as and when they're available. "Cybersecurity remains a constant, ongoing priority for Maersk," it added.