The group, also known as Fluffy Wolf, has been active since at least 2016 and has mainly targeted Russian companies with phishing emails designed to steal credentials, gain access to corporate networks and deploy malware. Russia's Interior Ministry said Monday that police had dismantled the group's infrastructure and identified its suspected members following an investigation conducted with assistance from cybersecurity firm Kaspersky.
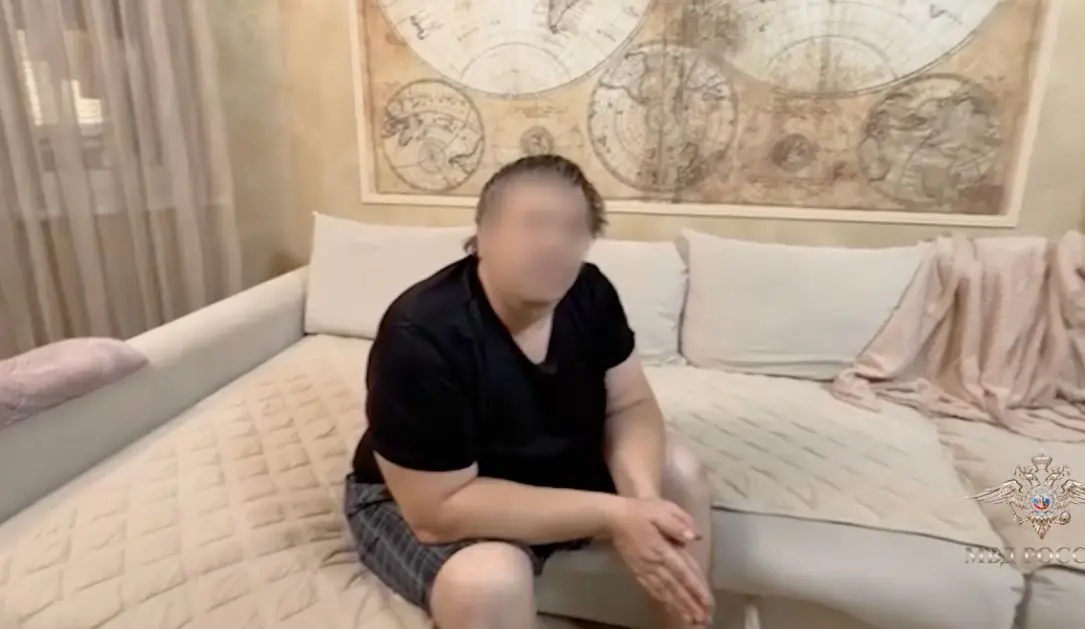
The group's alleged leader has been placed under house arrest, while two suspected accomplices have been released under travel restrictions, according to ministry spokesperson Irina Volk. Such arrests are unusual in Russia, where many well-known Russian-speaking hacking groups have operated for years despite being closely monitored by cybersecurity researchers and law enforcement agencies.