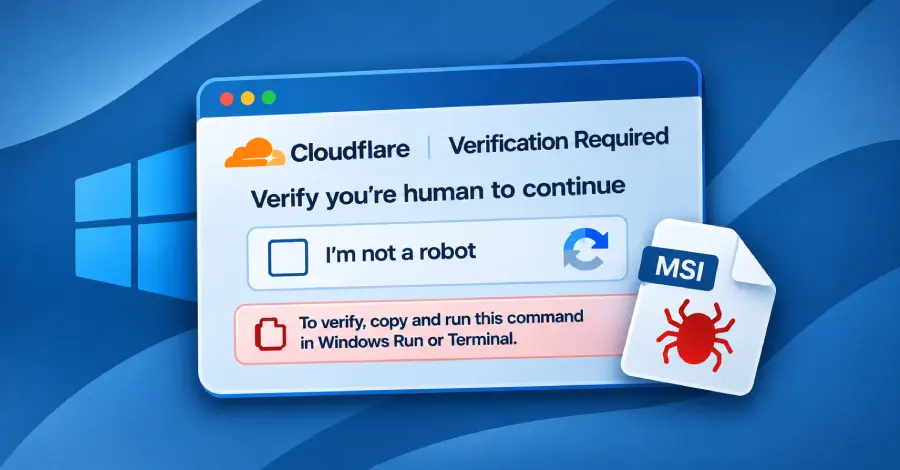
Blackpoint suggests that "ROMULUS likely operates as a delivery service, distributing CNCMachineRMS and Legion Loader through separate chains while retaining ClickFix and signed binary sideloading techniques."
This deployment mechanism indicates a sophisticated approach by adversaries, utilizing the ROMULUS ClickFix platform to introduce the previously undocumented RAT.
This activity reflects a broader trend among malicious entities in leveraging established delivery infrastructure to disseminate advanced malware payloads, impacting platform integrity and user security.