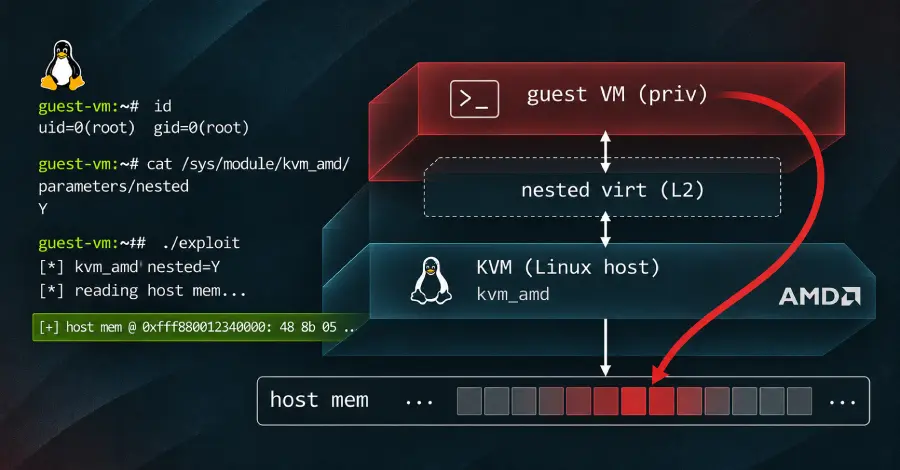
Researchers demonstrated that a vulnerability within KVM, the hypervisor integrated into the Linux kernel, permitted access to a substantial portion of a cloud server's memory from within a guest virtual machine running on DigitalOcean. Specifically, this defect, cataloged as CVE-2026-99312, allowed the reading of approximately 127 GB of memory. When operating on a shared server environment, this accessible memory space could potentially contain data belonging to other clients' virtual machines. This security weakness is exclusively present on host systems equipped with AMD processors and that have nested virtualization functionality activated. Patched kernel versions have since been distributed.
This type of vulnerability highlights the critical need for rigorous security auditing within foundational virtualization layers, directly impacting the isolation guarantees expected by platform operators and institutional users.
Why it matters
This vulnerability poses a serious isolation risk in cloud environments, potentially exposing sensitive data between tenants on shared infrastructure. Operators must verify their host hardware and virtualization configurations against this new CVE. Patching with fixed kernels is necessary to mitigate this memory access issue.