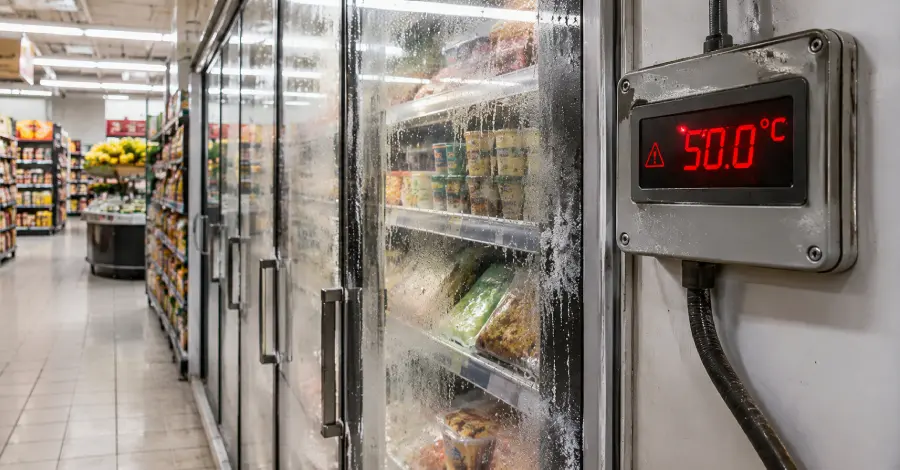
These threat actors are reportedly aiming to induce service interruptions, create fire risks, and result in inventory losses.
Specifically, the agencies noted that "The actors may exploit vulnerabilities or weaknesses in unpatched or internet-accessible controllers to remotely alter settings and force units into continuous heating."
This capability allows for remote manipulation of operational parameters within these critical cooling infrastructures.
The targeting of these systems highlights vulnerabilities within networked industrial control components.
This trend reflects a broader focus on the security posture of operational technology across various sectors.
Why it matters
This highlights critical security risks within industrial operational technology, specifically in cold-chain infrastructure. Operators must immediately assess the patch status and network exposure of their refrigeration controllers to prevent potential physical and inventory damage.