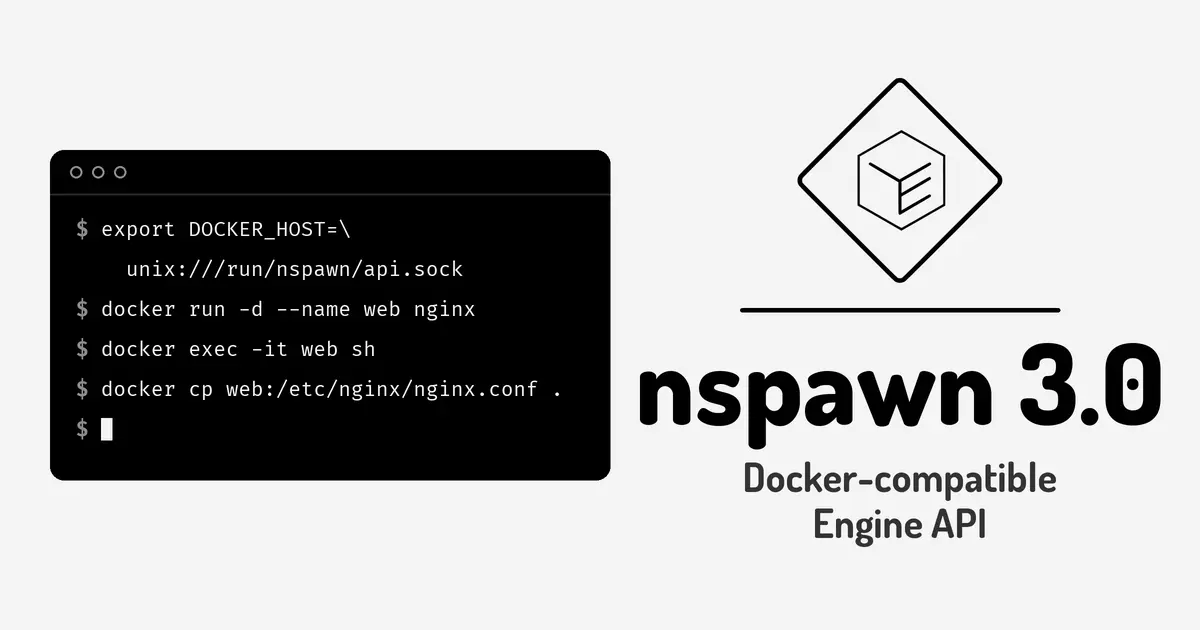
3.0.0 serves the API with its changes, on the host too. In between: The host’s socket is /run/nspawn/api.sock, opened by nspawn-api.socket. Its main purpose is compatibility: tools that manage containers through the Docker API, like GitLab Runner’s docker executor, can use nspawn’s machines instead. nspawn is still the command line for managing them, but the docker command works against the socket too.
The packages ship the socket turned off. Everything it does is a method of org.nspawn, under the same polkit actions: reads and waits need org.nspawn.inspect, logs and changes need org.nspawn.manage. Every user can connect, but polkit is never asked to prompt, since nothing on a socket can answer an authentication agent.
Root can do everything, and any other user needs a polkit rule, like nspawn-wheel.rules, which the packages ship as an example. As with the docker group, a user with org.nspawn.manage is root on the host: a machine runs commands as root and can mount any host path.