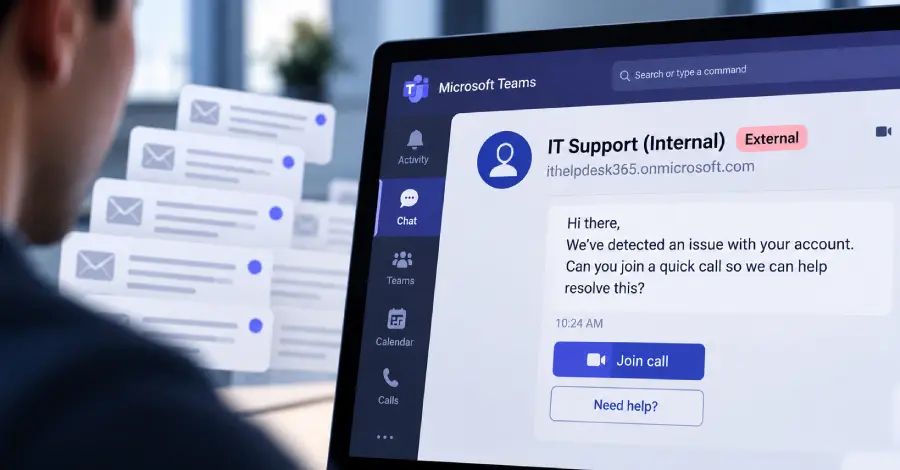
This mechanism is being exploited to execute impersonation scams or deliver malicious software.
Researchers have identified what they describe as a "recurring social engineering pattern" spanning hundreds of documented cases.
A consistent methodology has surfaced among the threat actors in these events. This includes the utilization of identical, disposable tenants.
Furthermore, the same specific phrasing, "'IT," is being employed in these attacks.
This pattern indicates a systematic approach by the malicious entities targeting organizational infrastructure.
These findings highlight an evolving vector for initial access, utilizing established collaboration platforms for malicious payload delivery.
Market participants must recognize this trend as a persistent threat against platform security.





