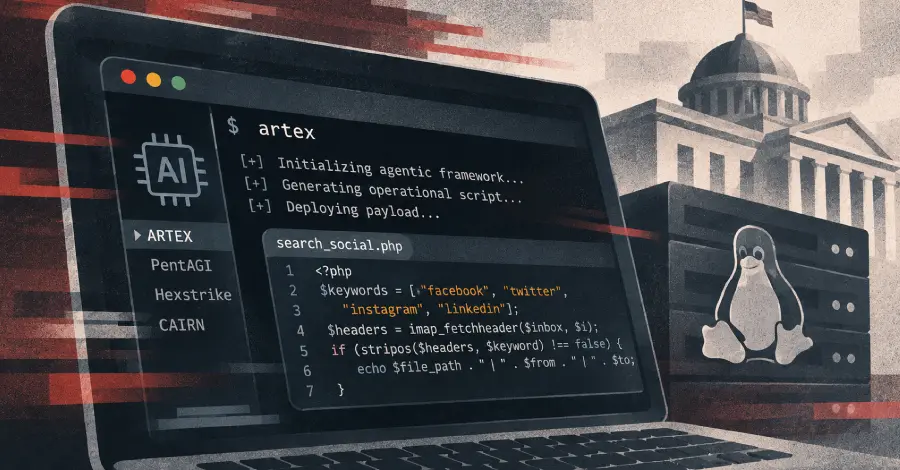
This campaign has been observed by Palo Alto Networks Unit 42 between the dates of October 2025 and April 2026, and its focus has been on Linux infrastructure linked to government organizations and state-connected systems.
This discovery highlights a targeted threat against critical infrastructure components running Linux. The involvement of sophisticated tools, such as SysGoRAT, alongside suspected scripts generated by artificial intelligence, underscores the evolving complexity of nation-state level cyber intrusions against operational platforms.