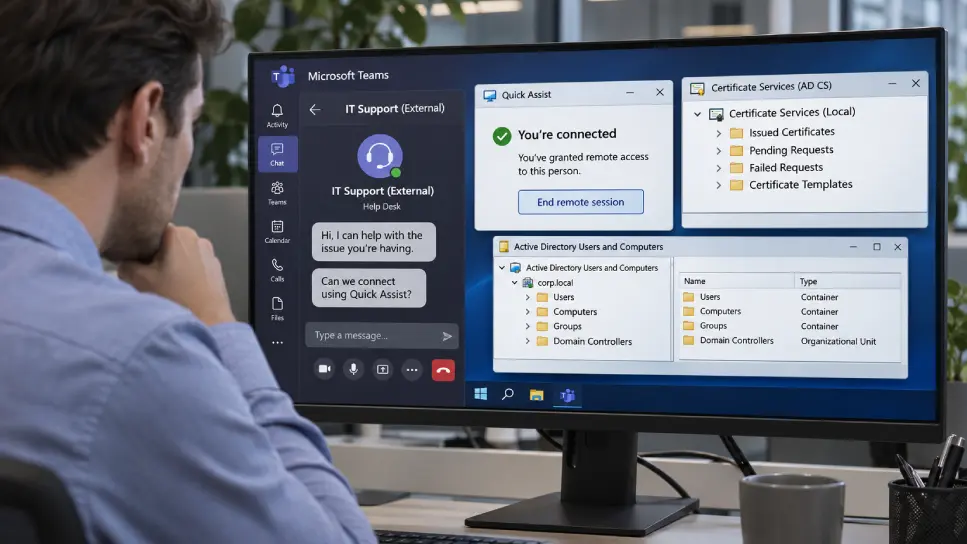
Subsequently, these malicious actors leveraged vulnerable configurations within Active Directory Certificate Services (AD CS) to acquire authentication certificates for high-privilege accounts, notably one belonging to a domain controller.
Microsoft has reported on these two security incidents, with one of the compromised entities suffering a significant outcome.
This pattern highlights vulnerabilities in how enterprise communication platforms intersect with internal identity and certificate infrastructure, presenting a critical vector for sophisticated lateral movement within corporate environments.