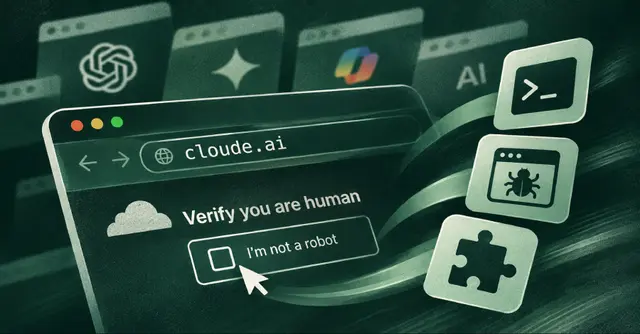
This malicious operation, which began around the middle of August 2026, has been targeting corporate personnel to steal active Google sessions. The perpetrator intentionally engineered the attack so that standard verification checks utilized by defenders would indicate the links were safe.
This campaign, active since mid-August 2026, is characterized by its ability to compromise live Google sessions belonging to employees within corporate environments. The adversary specifically structured their methods to bypass conventional security assessments that security professionals typically rely upon to validate link integrity.
The deployment of such sophisticated phishing techniques underscores an evolving threat landscape where attackers are actively developing methods to evade established defensive tooling. This demonstrates a persistent pressure on platform security mechanisms utilized by market participants.
Why it matters
This campaign highlights sophisticated evasion techniques targeting session security within corporate environments. Operators are exploiting trust mechanisms to bypass standard security tooling, posing a direct threat to platform integrity. Readers should watch for further analysis on how these live proxy attacks circumvent existing defenses.