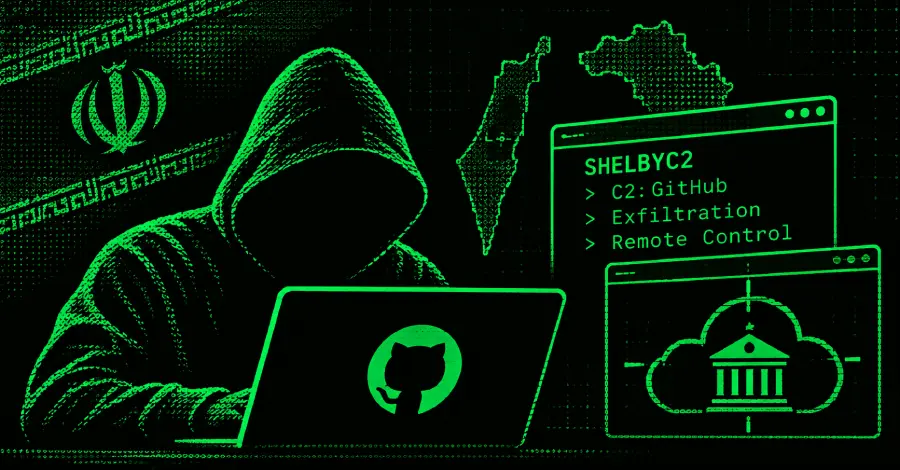
Details concerning this operation have been made public by cybersecurity researchers.
Dream Research Labs released a report detailing the activities of the threat actor.
This campaign resulted in the compromise of a prominent individual situated in Israel.
Furthermore, the operation caused additional security breaches impacting a government cloud infrastructure.
The findings illuminate targeted intrusions against critical national and regional entities.
This incident reflects a pattern of state-sponsored cyber activity directed at regional governmental and high-value targets.
Why it matters
This incident highlights the persistent threat of state-aligned actors targeting critical infrastructure and government platforms. Operators must review their cloud security posture against sophisticated espionage campaigns from regional adversaries.