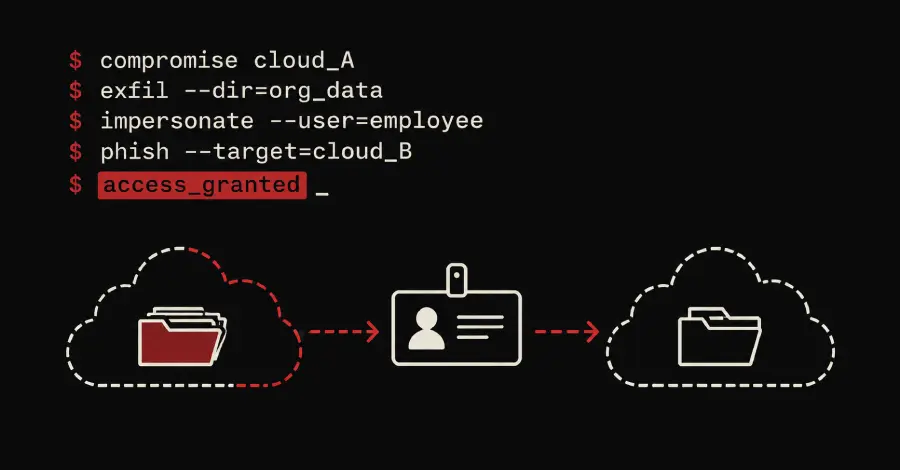
This cyber espionage collective, known as Cold Relic—and previously identified as COLDRIVER and UNC4057—has been documented using one cloud compromise as a starting point for multiple connected infiltrations that led to the compromise of other entities.
The observed tactic involves the threat actors leveraging stolen data from Google Workspace to facilitate these subsequent breaches.
This pattern illustrates a growing operational risk where initial access gained through a single platform vulnerability can cascade into widespread compromises affecting multiple downstream parties.
Why it matters
This highlights the critical risk of cloud service compromises acting as a launchpad for broader network intrusions. Operators must scrutinize third-party access and cloud data security to prevent supply chain attacks. The use of stolen Workspace data underscores the vulnerability of integrated enterprise platforms.