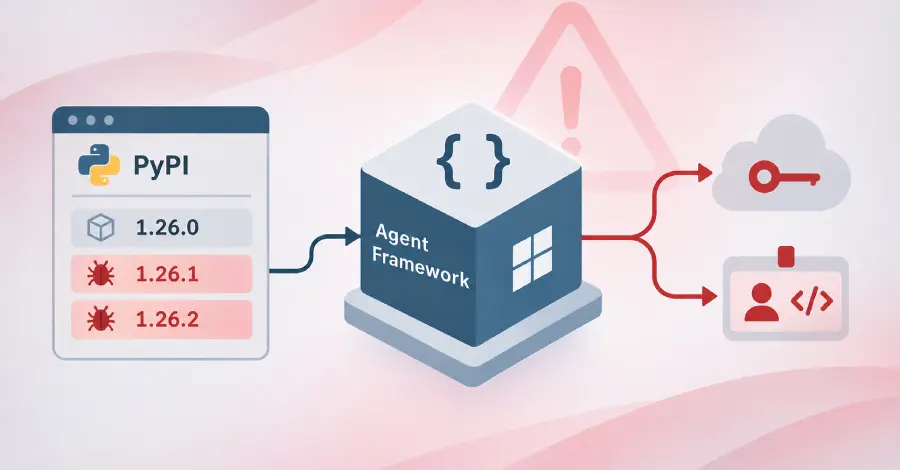
The compromised versions, specifically 1.26.1 and 1.26.2, were made available on November 17, 2026, with a thirty-three-minute interval separating their publication. These malicious releases are engineered to execute a credential stealer every time Python initiates.
This vulnerability, highlighted by Aikido, Chainguard, Endor Labs, OX Security, SafeDep, Socket, StepSecurity, and Wiz (a Google entity), presents a significant risk to platform integrity.
This incident underscores the ongoing challenges surrounding software supply chain security, where compromised packages can introduce sophisticated threats into operational environments.
Why it matters
This supply chain attack directly impacts software dependencies used across various infrastructure deployments. Operators must immediately audit dependencies to ensure no vulnerable versions of this framework are running in production environments. The risk involves the theft of sensitive cloud credentials.