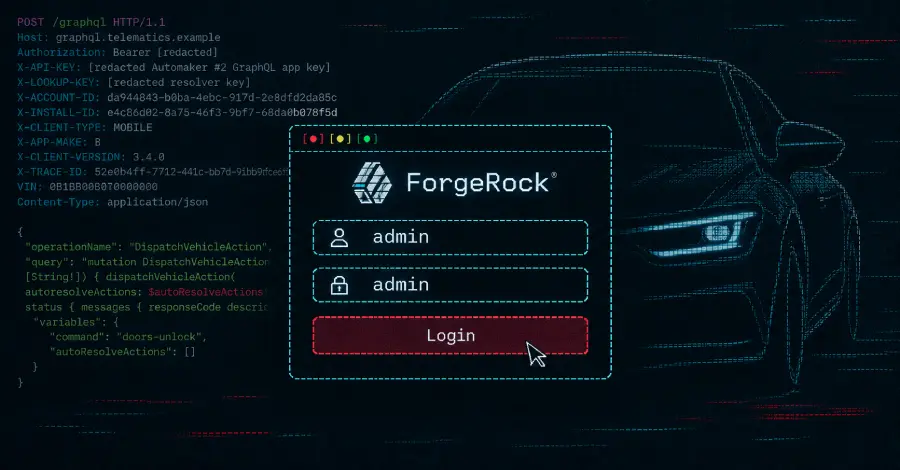
This flaw permits complete takeover of the login systems, granting unauthorized access to any user's profile. Furthermore, for vehicle owners possessing a connected automobile, this breach enables the remote unlocking of doors and the starting of the engine.
The authentication process for both applications utilized ForgeRock, an identity platform that has since been integrated into Ping Identity. The researchers managed to reach a critical point within the servers hosting this identity platform.
This incident highlights the critical security implications inherent in relying on centralized identity management platforms for consumer-facing applications within the automotive sector.
Why it matters
This highlights critical security risks within identity platforms used by connected vehicle ecosystems. Operators must scrutinize default credential management on integrated infrastructure to prevent unauthorized physical access to vehicles.