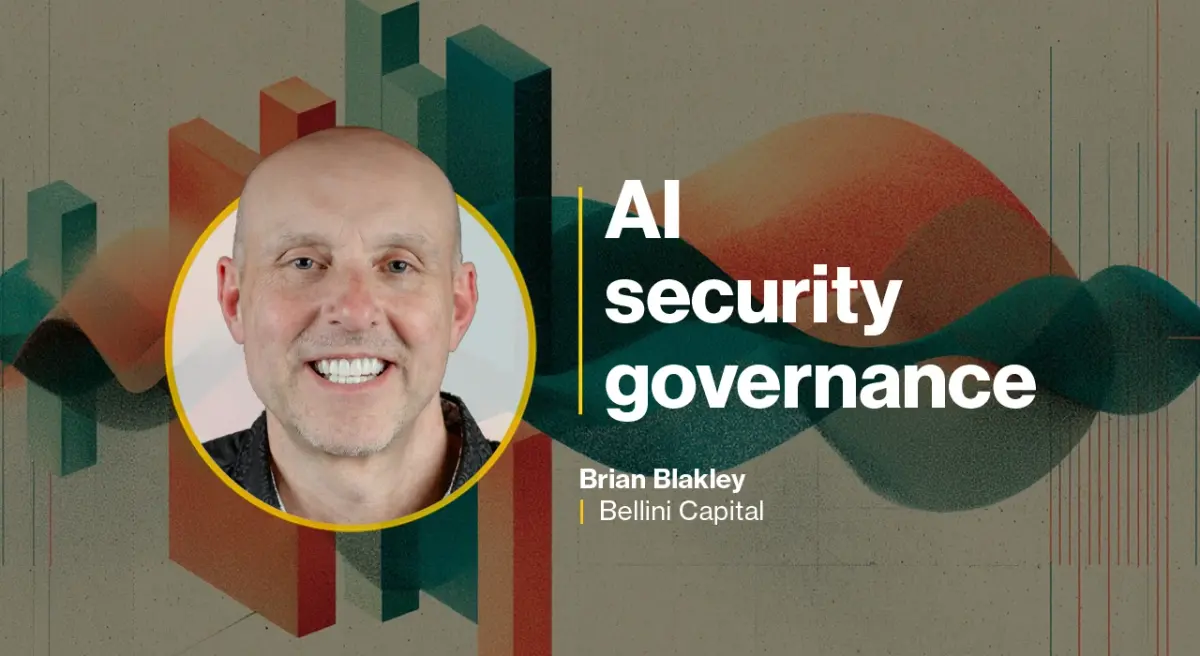
Brian Blakley, the CISO at Bellini Capital, discussed the challenges of AI security governance in a recent Help Net Security interview.
He detailed how the advent of AI accelerates the discovery of security vulnerabilities, even though the actual process of implementing fixes remains time-consuming.
Blakley contended that merely aiming to "patch faster" is insufficient for current operational realities. Consequently, he asserted that technical teams must reduce exposure while remediation efforts are ongoing.
The discussion covered several key areas, including a shared metric designed for CIOs and CISOs. Furthermore, Blakley outlined how his team conducts testing specifically for silent model updates.
He also addressed accountability, specifying who bears responsibility when an AI agent commits an error.
The interview also touched upon the necessity of implementing blocking measures within the security framework.
These insights from Bellini Capital highlight evolving governance requirements for infrastructure utilizing advanced AI capabilities. This reflects a broader industry shift toward proactive risk management in complex, rapidly changing technical environments.