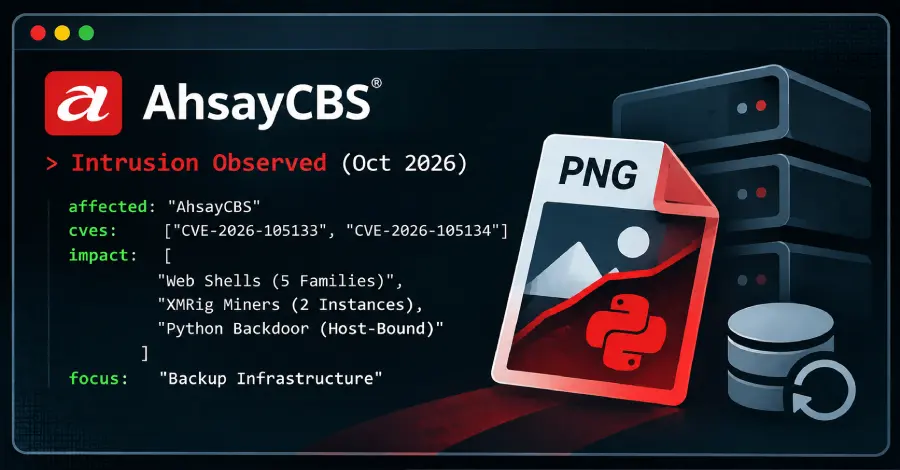
Huntress detected this malicious operation during October 2026. This activity specifically involved chaining vulnerabilities CVE-2026-105133 and CVE-2026-105134, which allowed threat actors to circumvent authentication mechanisms and run unauthorized commands on compromised infrastructure. Patches addressing these two flaws are now available.
This incident highlights the persistent threat posed by vulnerabilities within widely used enterprise software, presenting a critical risk vector for platform integrity.