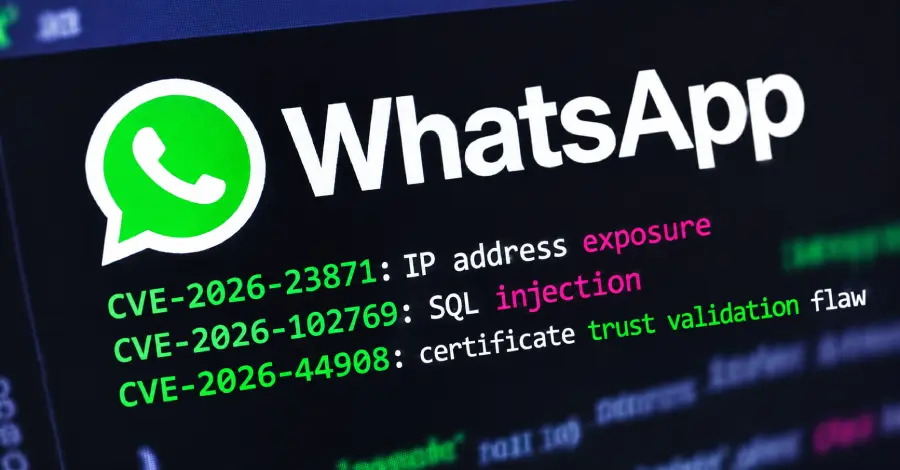
One of these flaws specifically affects the Android version and is suspected by the platform to have been leveraged in scam communications.
This specific vulnerability is identified under the tracking number CVE-2026-23871.
The issue involves insufficient validation of external ad-reply URLs within WhatsApp for Android and WhatsApp Business for Android versions prior to 2.26.17.4.
This deficiency represents a potential vector for compromise within the messaging infrastructure.
The remediation effort by the platform addresses these critical security gaps across its mobile deployments.
This incident highlights ongoing operational risks related to third-party content handling within widely adopted communication platforms.
Why it matters
This patch addresses a critical flaw in how WhatsApp handles external links, which poses a direct risk to platform integrity. Operators must ensure their infrastructure is updated to the latest version to mitigate potential exploitation vectors used in phishing campaigns.