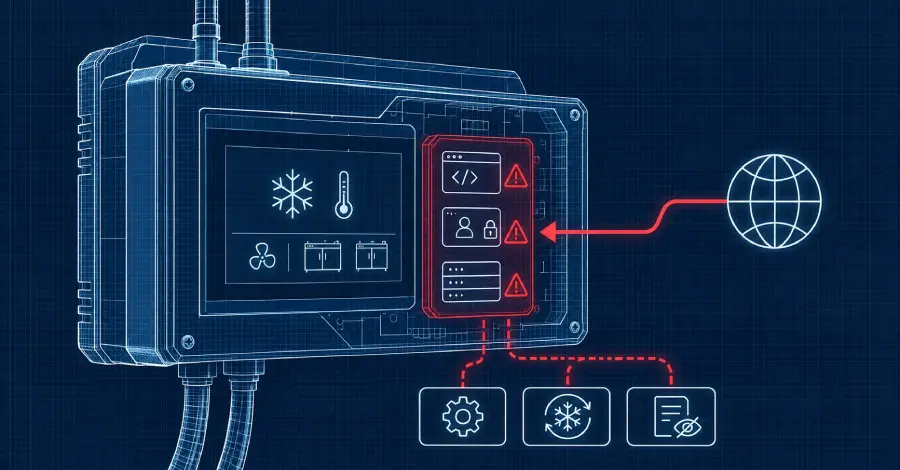
These weaknesses potentially permit an external threat actor to gain control of a controller without needing to authenticate. Furthermore, the researchers noted that the most recent firmware iteration, version 5.4.0, does not resolve these issues, and currently, no corrective patch has been released. In response to this discovery, governmental cybersecurity bodies in Germany, Ireland, and Belgium issued advisories this week urging operators to take protective measures.
The lack of available remediation, even in the latest firmware, presents a significant operational risk for infrastructure utilizing these specific controllers. This situation reflects a broader industry challenge concerning the timely patching and securing of embedded industrial control systems against remote exploitation.
Why it matters
Operators managing critical infrastructure using these controllers face an immediate, unmitigated remote takeover risk. Since no patch is available, organizations must urgently review their network segmentation and access controls around these devices. This highlights the persistent security challenges in industrial control systems.