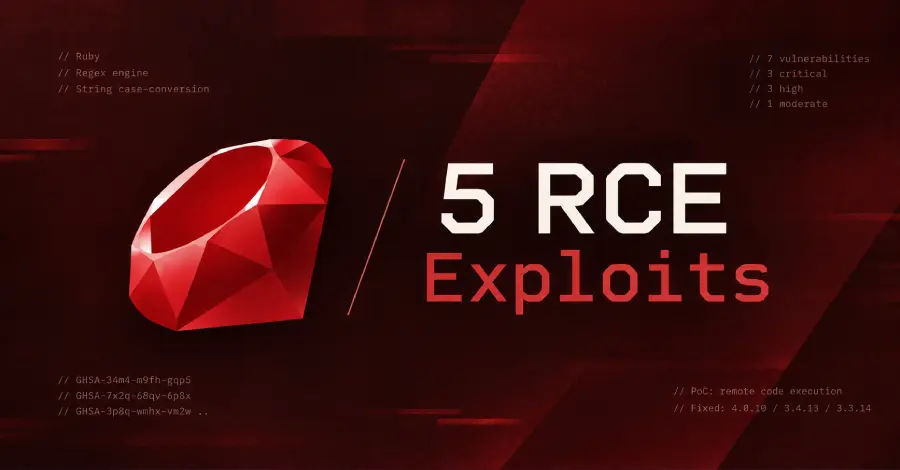
Maintainers of the Ruby project have issued patched versions addressing seven instances of memory safety vulnerabilities found within the language's string case-conversion logic and its regular expression mechanism.
Specifically, the project's custodians have indicated that for five of these identified issues, demonstrations exist showing that specially constructed input allows for code execution on the host system. The maintainers explicitly stated, "We are aware of PoCs that prove some of them can be used to trigger remote code execution."
These vulnerabilities reside within two distinct components: the regular expression engine and the code responsible for string case conversions.
The disclosure of these flaws highlights ongoing security considerations within foundational language implementations, where subtle memory management issues can escalate to critical remote code execution vectors.
Why it matters
For operators running Ruby applications, these flaws present a critical security risk, potentially allowing remote code execution via crafted input. Immediate patching is necessary to mitigate exploitation vectors in production environments.