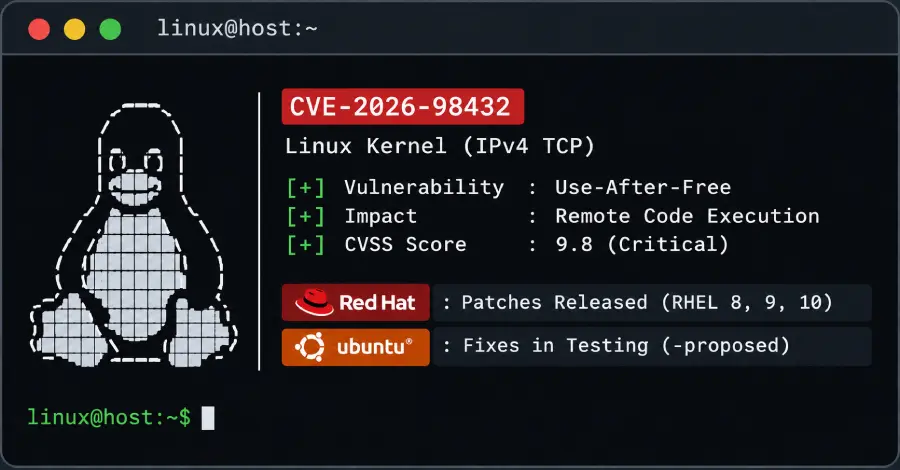
Conversely, the remediation patches for Ubuntu's three most recent long-term-support distributions are currently situated within an opt-in testing channel, and there is no specified timeline for their general release. This vulnerability, cataloged under CVE-2026-98432, presents a risk because an attacker who is not authenticated can exploit it remotely.
This situation highlights differing release cadences among major operating system vendors regarding the deployment of critical security patches for kernel-level networking components.
The availability of these patches is significant for platform operators managing infrastructure reliant on these specific Linux distributions.
Why it matters
This highlights differing patch release cadences between major Linux distributions, which impacts immediate operational security for infrastructure operators. Organizations relying on Ubuntu must monitor the testing channel closely for when these critical fixes become generally available.