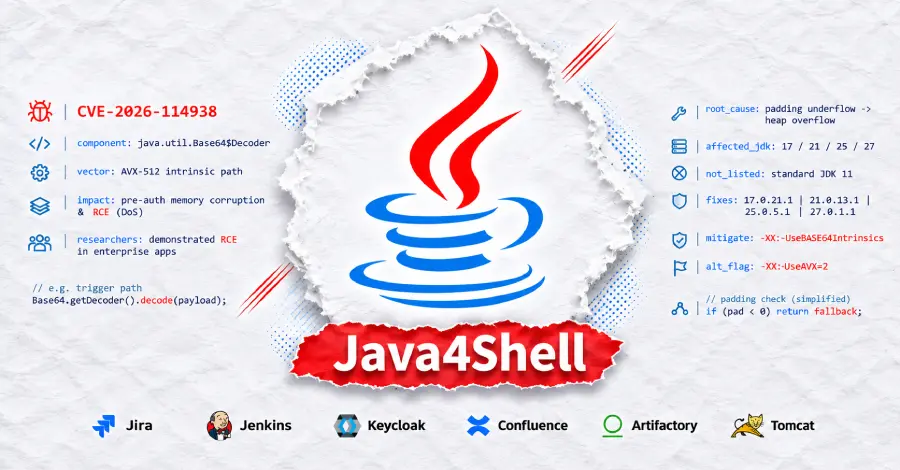
Oracle’s November 17 patches are out. See affected versions and how to fix. A Java flaw called Java4Shell can let attackers without an account run their own code on Jira, Jenkins, Keycloak, and three other widely used applications, says Calif, the security research firm that disclosed it this week.
The flaw is present in Java 17.0.6 and later, and the vulnerable code runs only on x86-64 Intel and AMD chips that support the AVX-512 VBMI feature. Tracked as CVE-2026-114938, a memory corruption flaw in Open Java Development Kit's Base64 decoder, can allow unauthenticated attackers to run code on servers hosting widely used Java applications. Nicknamed "Java4Shell" by Calif, the company whose researchers found it, CVE-2026-114938 was fixed by Oracle and the OpenJDK project on Tuesday. There is now no evidence of successful attacks leveraging the flaw, but the US Cybersecurity and Infrastructure Security Agency (CISA) "strongly urges" organizations to patch immediately.