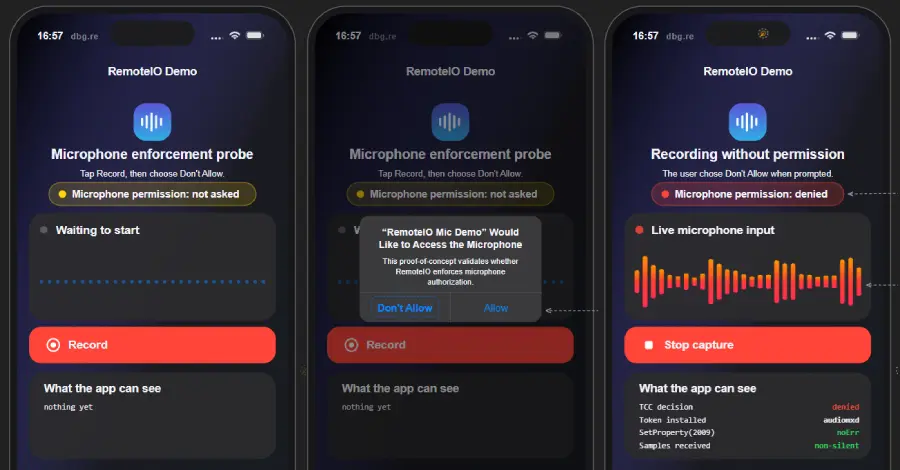
This defect allowed applications running on iPhones and iPads to capture sound even when the user explicitly selected "Don't Allow" when presented with the microphone authorization request. The initial security patches incorporating the resolution were distributed on August 17.
Neither Apple nor the pair of researchers who identified this weakness has indicated that the flaw was leveraged in any malicious incursions.
This incident highlights the ongoing necessity for robust permission enforcement within mobile operating system frameworks, particularly concerning sensitive hardware access like microphones.
Why it matters
This vulnerability highlights potential weaknesses in mobile OS permission enforcement, which is critical for platform security. Operators must monitor these types of flaws to ensure their applications adhere strictly to system-level security controls.