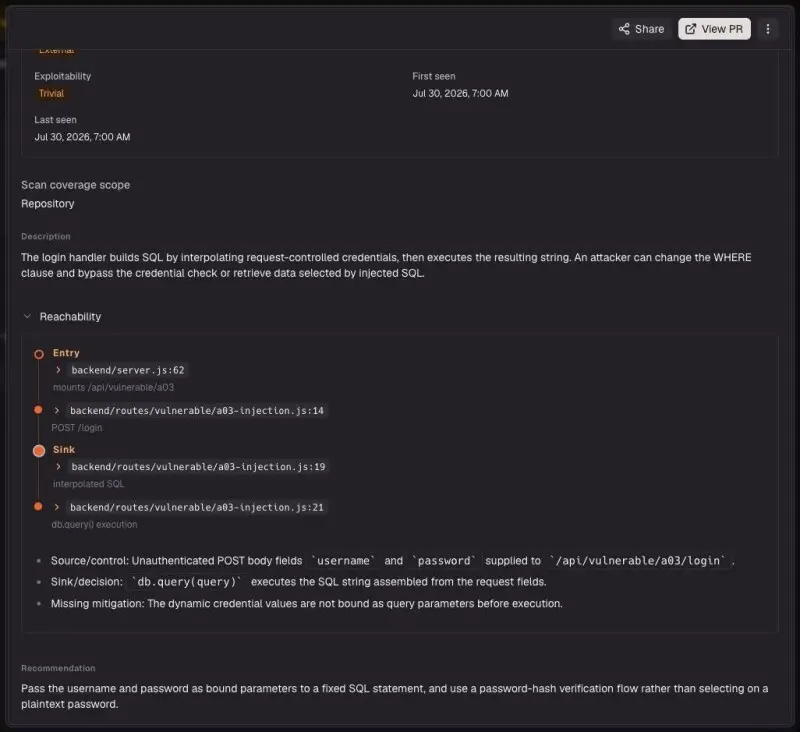
AI agents are investigating unfamiliar systems, testing ways to get in and adjusting their next move when an attempt fails. Anyone with a credit card can use that capability to come after your application.
Coding agents and their tool integrations have introduced new entry points and surface areas that can be exploited. Pillar’s OpenCode disclosure in October showed how a malicious Model Context Protocol (MCP) server could execute commands on a developer’s Windows or WSL machine during authentication.
A server-supplied URL reached a shell without tricking the model. In the same month, the discovery of the two PHP2Shell vulnerabilities, remote code execution bugs in the PHP runtime uncovered with the help of OpenAI’s models, brought new urgency to securing longstanding code across much of the internet.