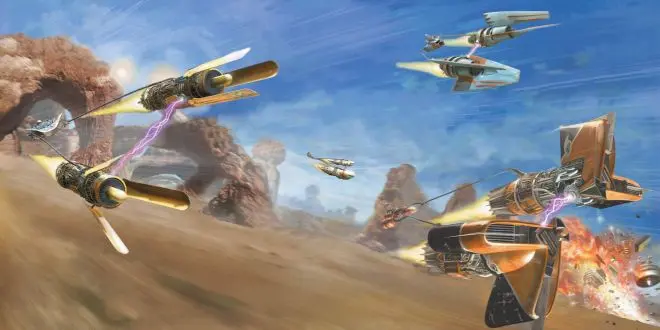
The player pilots a podracer, just like in the movie Star Wars: Episode I – The Phantom Menace. This article details the multiplayer protocol and a vulnerability allowing remote code execution. We will also cover creating a Wireshark dissector and developing tools with DirectPlay.
Star Wars Episode I: Racer is a racing video game developed in 1999 by LucasArts. It is based on the podrace scene from the movie Star Wars: Episode I – The Phantom Menace. The research focused on version 1.0 distributed by GOG for the Windows platform.
This article details the analysis of the protocol used for local network multiplayer. The game is installed on two virtual machines on the same network. The network capture below, displayed with Wireshark, shows the packets sent when a player (at 192.168.56.2) connects to a game host (192.168.56.104). The game communicates in multiplayer mode over UDP on destination port 54792.