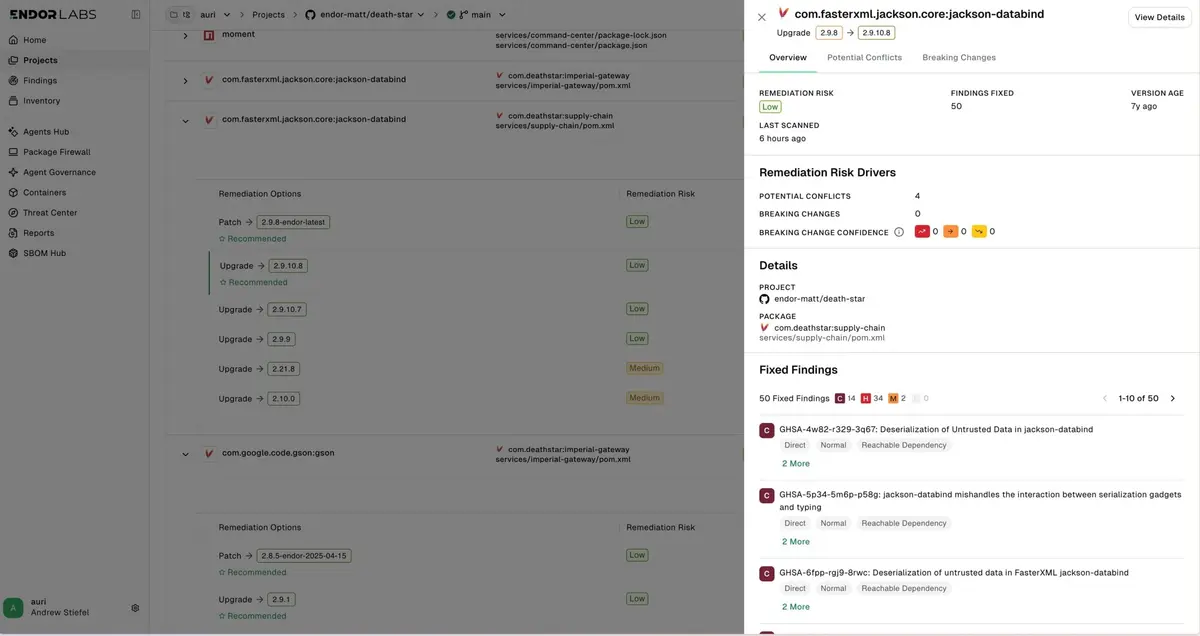
Joe Harrington, a principal product manager for Endor Labs, said AURI Fix for Open Source provides DevSecOps teams with an autonomous remediation engine that enables them to apply small amounts of highly targeted code to remediate vulnerabilities. That capability is critical at a time when advanced AI models are discovering thousands of vulnerabilities in open source code that cybercriminals can now exploit in a matter of minutes using AI tools of their own, he noted.
Without the aid of AI tools, it's simply not going to be possible for DevSecOps teams to manually keep pace with the number of vulnerabilities that need to be investigated and ultimately fixed, added Harrington. Making matters worse, the mean time to exploitation for vulnerabilities is already at 39 days and continues to decline, he noted.