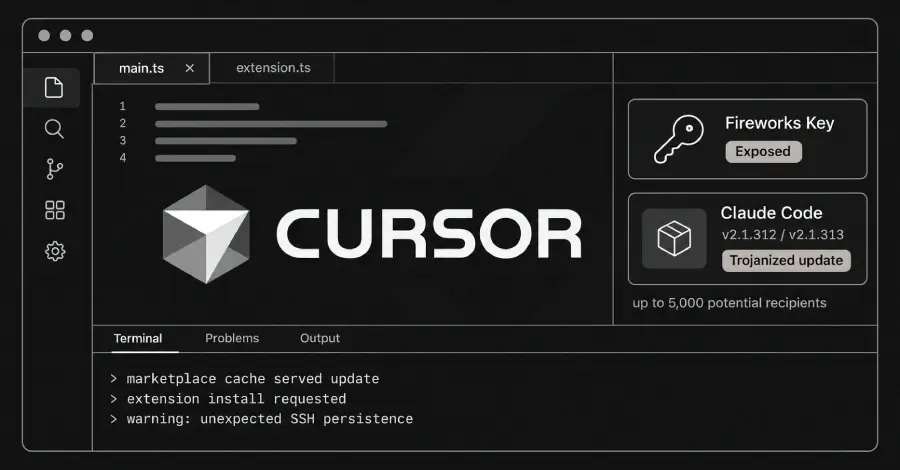
A breach targeting Fireworks AI led to the theft of an access key, which subsequently resulted in the compromise of Anthropic's official Claude Code extension available on Cursor's extension marketplace.
Cursor reported in a Friday update that "An attacker obtained an access key we had issued to Fireworks." Furthermore, the key became exposed through the Fireworks incident, enabling the malicious actor to duplicate information from a read-only source.
This sequence of events highlights a critical dependency risk where the security posture of one third-party service, in this case, Fireworks AI, directly impacts the integrity of integrated platforms like Cursor. The incident underscores the operational necessity for rigorous key management across interconnected software ecosystems.
Why it matters
This incident highlights critical supply chain risks in developer tooling, where a vulnerability in one service can compromise integrated platforms. Operators must closely monitor third-party dependencies for key exposure and unauthorized access vectors.