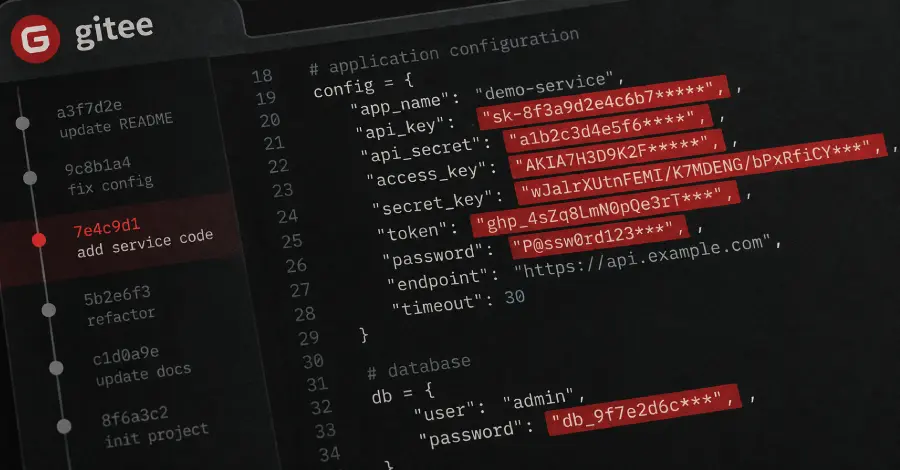
An independent researcher, Ben Zimmermann, discovered that 26,400 credentials, which developers had inadvertently placed in publicly accessible code on Gitee, a Chinese code-hosting platform, remained functional upon testing. These exposed credentials, which could have been exploited by anyone who copied them from the code, were identified after Zimmermann scanned 7.25 million public Gitee repositories and subsequently announced his findings on October 28. The majority of these compromised credentials were keys pertaining to cloud and AI services.
This incident highlights significant risks associated with the improper management of sensitive access information within publicly exposed development repositories.