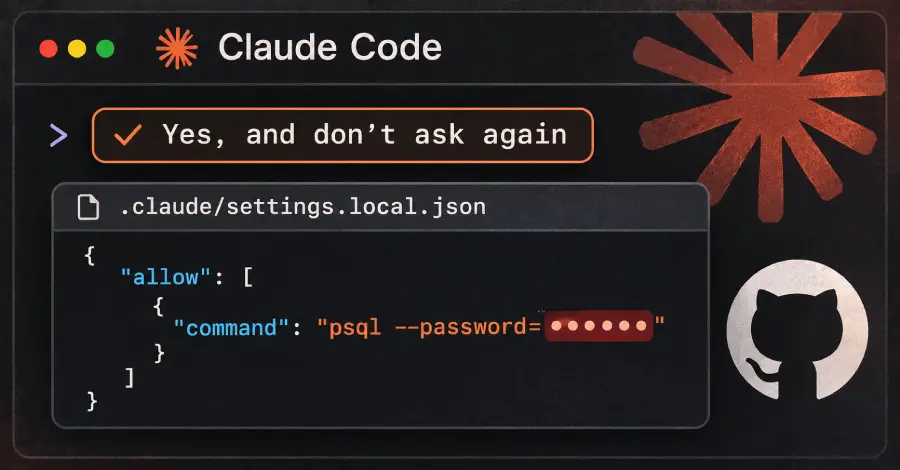
This vulnerability arises because when a user opts to select "Yes, and don't ask again," Anthropic's AI coding assistant has the capability to store the command verbatim, including any sensitive secrets, within a project settings file.
Yesterday, the software security firm Apiiro reported this discovery, detailing that 1,122 public instances of this exposure were found.
This incident highlights potential risks associated with integrating advanced AI coding assistants into development workflows, particularly concerning the persistence of credentials within version control systems.
Why it matters
This incident highlights significant risks in AI coding assistants where user input, including secrets, can be persisted publicly. Operators must closely monitor how their development platforms handle sensitive credentials passed to generative AI tools.