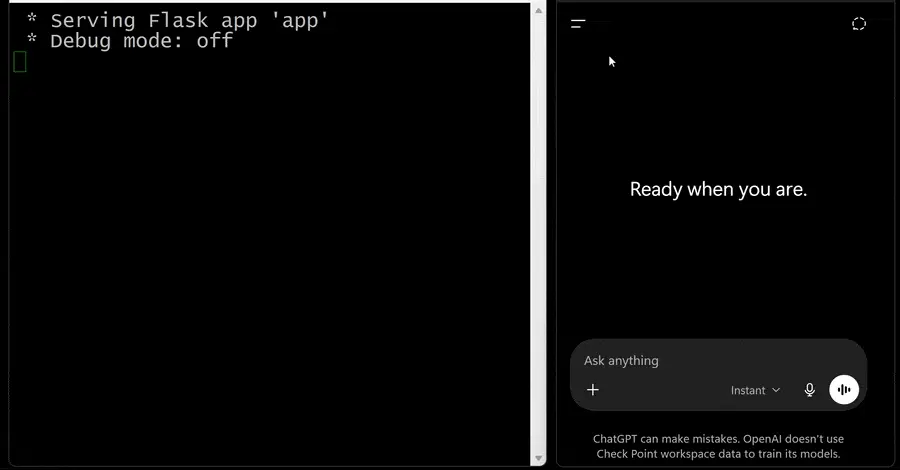
This vulnerability, which has since been addressed, presented a pathway for unauthorized data extraction.
Lockdown Mode, an optional feature implemented by the artificial intelligence firm, was rolled out in June 2026 with the aim of mitigating dangers of data leakage stemming from prompt injection techniques. The researchers noted that "The flaw could enable silent chat data theft, phishing," indicating the potential for covert compromise.
This incident highlights the ongoing necessity for robust security controls in generative AI platforms, as even optional protective measures can possess exploitable weaknesses. Market participants and institutions must remain vigilant concerning the evolving threat landscape surrounding large language models.
Why it matters
This highlights ongoing security risks within major AI platforms, even with protective features enabled. Operators must monitor how these bypass methods might affect their deployed AI infrastructure and data integrity.