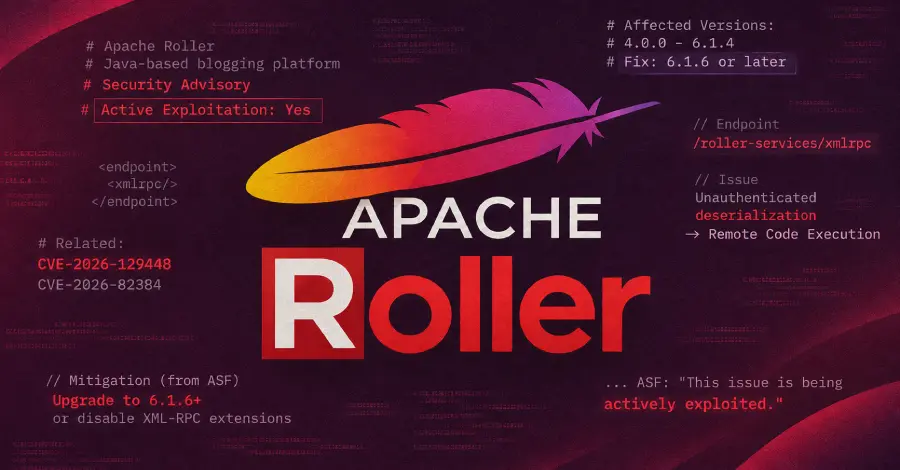
Apache Roller is an open-source, Java-based blogging platform.
This flaw is identified as CVE-2026-129448, carrying a CVSS score of 9.8.
The issue involves unauthenticated deserialization occurring within the XML-RPC endpoint. Such a vulnerability presents a pathway to remote code execution.
The nature of the exploit is described as "Deserialization of Untrusted."
This development underscores ongoing risks associated with maintaining security posture across utilized open-source infrastructure components.